Android's Next-Gen Enclave for On-Device AI
Devices are shifting from collections of standalone apps into proactive, personal assistants that anticipate needs, streamline complex tasks, and act on our behalf. To make these assistants truly helpful, it relies on a user's data —which may include an on-device knowledge graph that connects the dots across emails, messages, calendar events, and cross-app interactions. Centralizing this on-device digital context makes safeguarding it paramount.
Android already provides robust application sandboxing and SELinux policies to protect and isolate user data. To strengthen this further, today we are introducing Android on-device AI seal (also known as AISeal): Android’s enclave architecture for personalized on-device AI experiences. Built on the Android Virtualization Framework (AVF) and the protected Kernel Virtual Machine (pKVM) hypervisor, On-device AI seal enables a hardware-isolated, centrally managed secure vault (utilizing protected VM) that decouples sensitive AI workloads from the host operating system—designed so that even in the event of a full host OS compromise, personal data remains cryptographically isolated and protected from unauthorized access.
An Open, Multi-Tenant Vault for On-Device Intelligence
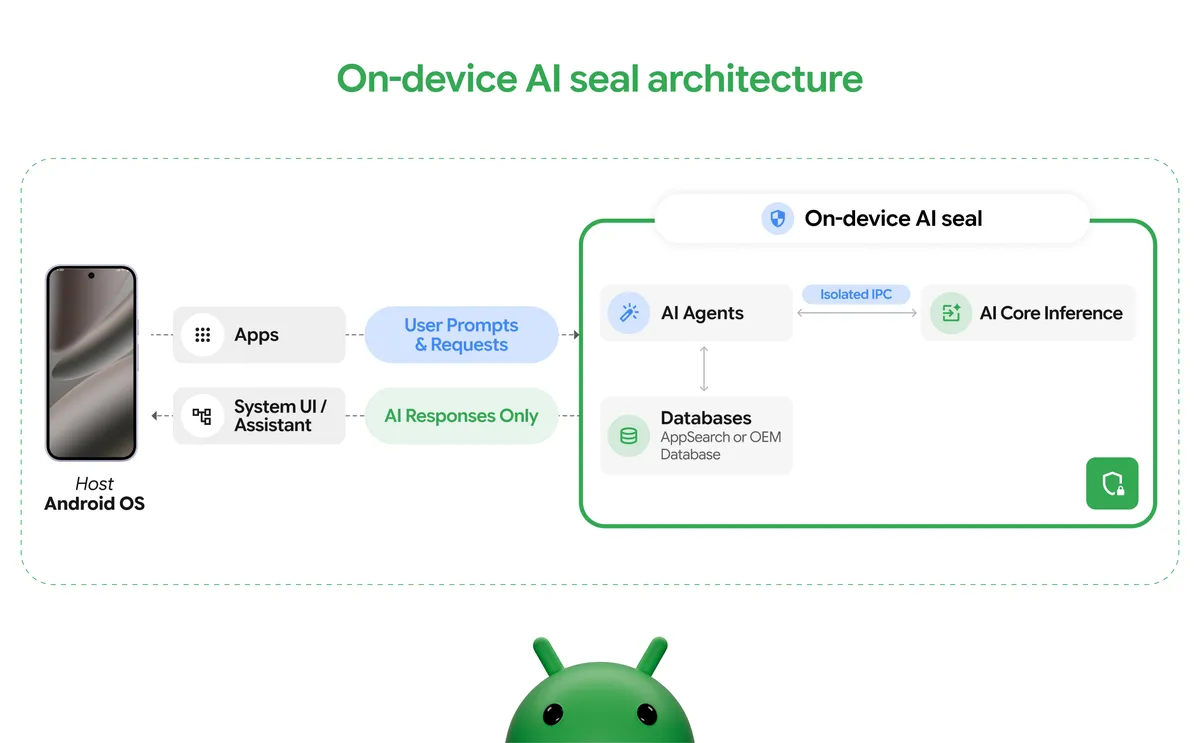
Designed for mobile efficiency, we are enabling a multi-tenant protected environment that delivers robust hardware isolation while optimizing system memory and battery life. Through this multi-tenancy capability, the following diverse AI services can safely share a single secure vault without compromising isolation:
- Protected databases: Securely stores and indexes personal context in encrypted local storage. On-device AI seal currently uses AppSearch as an optimized reference implementation, while supporting any database—including an OEM's proprietary store.
- On-device inference: Designed to execute foundation models locally via future integrations with AICore.
- AI agents: Built to assistants that combine private context with local inference to perform helpful tasks.
Internal access controls allow these components to work together safely without exposing raw data. For example, an assistant can query the database and run an inference to summarize your schedule entirely inside the vault—while strict outbound controls are designed to allow only the final, intended answer to cross back to the main operating system.
Ecosystem Momentum
Delivering meaningful mobile security requires deep co-engineering across silicon, operating systems, and device manufacturers. This enclave architecture establishes that trust through Android Virtualization Framework (AVF). Our foundational open-source implementation is anchored in the protected KVM (pKVM) hypervisor—delivered via Android's Generic Kernel Image (GKI) and certified to SESIP Assurance Level 5 (AVA_VAN.5), the industry's highest vulnerability testing tier under ISO 15408.
Commercial momentum of this technology is already underway. MediaTek recently announced support of the pKVM-backed On-device AI seal on MediaTek Dimensity 9600 Pro, and Qualcomm’s Snapdragon chipsets will also support our architecture via AVF as we expand across the broader silicon ecosystem. At the same time, we are working with device manufacturers, to put these capabilities into practice, powering next-generation experiences.
The Horizon: Expanding In-Vault Intelligence
Currently, we are establishing hardware-isolated personal context storage as our foundational milestone, actively rolling out across Android.
Looking ahead, we are continuing to work with silicon and OEM partners to bring the entire on-device AI lifecycle inside the protected vault, including:
- In-vault inference and autonomous agents: Moving model execution and system-level agents directly into the pVM, ensuring sensitive context is processed without ever touching host memory.
- Direct NPU device assignment: Granting the enclave a direct, private hardware lane to the on-chip NPU so AI models run at full silicon speed.
- Confidential cloud extension: Enabling end-to-end encrypted hybrid inference between on-device pVMs and OEM’s own confidential cloud servers.
Together with our partners, we are establishing an open enclave standard for on-device AI across the mobile industry: powerful, proactive intelligence built on uncompromising, hardware-backed trust.